 Posted by
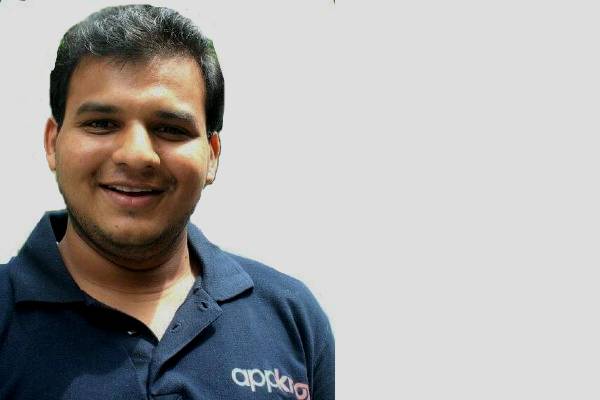
With nearly six million mobile apps in circulation today, mobile app security has become a major concern for users. Android users have access to over 3.48 million apps on Google Play, while iOS users can choose from around 2.22 million on the App Store. But how many of these are truly secure, tested against data leaks, malware and cyberattacks? CEO Harshit Agarwal and Co-Founder and CTO Subho Halder lead Appknox to fill that gap.
In this in-depth interview, Harshit Agarwal CEO of Appknox talks to TechHerald about the niche of mobile app security, his company’s app security testing platform, offerings and concerns of enterprises as well as customers and the usage split of the Appknox platform between Andriod and iOS apps.
He also discusses the maturity of mobile app security testing, the emergence of DevSecOps, competitors and Appknox‘s differentiator, business growth and more.
Edited excerpts…
Q1. Can you brief us about Appknox?
Harshit Agarwal: Appknox is a mobile application security testing company started in 2014. I started Appknox with my Co-Founder Subho Halder and we have focused on the niche of mobile app security, that’s our forte. We have built a platform that helps enterprises, Fortune 500 companies or any organisation with upwards of 30-40 mobile applications to make sure their applications are secure when they release the subsequent versions of their apps. That’s our key offering. We work with more than 500 enterprises globally and help them secure their mobile applications. Among them are some Fortune 500 companies and top banks. In India, we work with four out of five top private sector banks.
Q2. Appknox mainly focuses on mobile app vulnerability assessment and penetration testing (VAPT). Brief us about the testing solution and how you are serving the customers?
Harshit Agarwal: Primarily, we offer our cloud-based testing platform to enterprises. But we also work with Fortune 500 companies and government agencies. Some of these organisations don’t prefer the cloud, so offer them the on-premise solution. We have done a couple of on-premise deployments in the Middle East, India and Europe.
Primarily, these are either government agencies, banks or Fortune 500 companies, where very critical apps are getting uploaded, and they’re not fine with cloud-platform. For these three domains, on-premise is required. And the rest of the customers are on our cloud. We currently have done 25 odd on-prem deployments out of 300 active customers. We have served 500 plus enterprises to date.
Q3. While using the Appknox platform, what are the major concerns of organisations or app developers?
Harshit Agarwal: These customers, primarily have the challenge around their regular release of mobile app security. The traditional way of doing VAPT is going to any of these Managed Security Service Providers (MSSPs) and asking them for mobile app security testing. They would take the app and run it through a manual process as part of services, which takes roughly 5 to 7 days.
The timeline of 5 to 7 days of security testing is impossible with the new updates being released every one to two weeks. So till now, companies used to either skip app security testing or run it in parallel and look at those issues in the subsequent release. But that would mean those apps on the Play Store might be vulnerable and, if the user is not updating the app, then that particular user is using the vulnerable app, which can lead to a lot of data loss and more.
We’ve automated security testing to cover up to 80% of the entire VAPT process. The remaining penetration testing (PT) typically takes just 1 to 2 days. This approach ensures about 80% of the process is completed within 90 minutes. As soon as developers build the app, they can not only release it quickly but also identify whether it’s broken and exactly where. They can then fix the issues immediately and push the release, without delays caused by extended security checks.
Q4. How is Appknox’s usage split between Android and iOS mobile applications?
Harshit Agarwal: Ideally, I think that (usage) split remains 50/50. The major reason is, as a user, sometimes we feel that we are using an iPhone, so the app is supposed to be more secure. But that’s not the case. When it comes to (Google) Play Store, they will only check whether the app is malware or not and that’s it.
If you’re using Flipkart, they do not look if Flipkart is vulnerable or not? They will not look in-depth because it’s not possible. Play Store is managing upwards of 5 to 7 million apps, so looking at and ensuring security for that many numbers of apps, is impossible. It’s not humanly possible and whatever checks they do are basically at configuration level only and are very basic checks. Still, in that case, iOS apps are more secure but when it comes to business-level apps and all that’s not the case.
On contrary, at times we have seen that some of the apps are a little more vulnerable on iPhone than on Android. Developers primarily build on Android using Java, while they use different technologies for iPhone, which often creates more gaps in iOS apps. Overall, I would say that vulnerability and the app split remain 50/50. There is no difference in whether we are scanning Android or iOS. The way we do it all is different, but overall it remains the same.
Q5. Compared to those app stores, is there any difference in how enterprises test the security of mobile apps?
Harshit Agarwal: Yes, definitely it is different. For example, we do work with some of the Fortune 100 companies. They use common apps like LinkedIn and others, which are scanned by app stores. But still, when it comes to enterprises, they have to ensure their internal data don’t get leaked through the apps. For example, enterprise team members use the Workday app as a workforce management tool.
Big enterprises must now ensure their internal data on the app, such as team members’ salaries, does not leak to competitors. Because that will be very, very critical data for them to lose. If they rely only on the Play Store, it checks only the app’s permissions, SSL encryption, and some basic features. Now leaving it on that itself is a risky bit. The Workday app also allows these enterprises to do a further VAPT at their end to make sure that their internal data is secured. This is one example.
Similarly, there are a lot of apps these enterprises use. While working with these enterprises, we ensure to check these apps on their behalf and tell them whether their data is secured or not. Mostly, we have found that these big companies are quite secure because they go through regressive testing. When enterprises look at any app for their internal compliance bit, they ensure the data is secured. They have to get it done using a platform like ours because it covers the 360 degrees of mobile app security.
Q6. Besides, the Appknox platform, are you also offering different services to the needs of enterprise customers?
Harshit Agarwal: We do offer services in two models. The primary is related to mobile security only. A lot of these enterprises, want manual PT also to be done, which takes only two days. But they don’t have internal bandwidth or capability and in some cases, it’s not humanly possible. For example, one of our biggest enterprise customers manages and builds over 650 mobile apps globally through separate teams. They have outsourced most of the development.
Now, if that company has to look after security testing, it would need a big team of security to coordinate with all of it. And since we have platform-driven services, it’s easy to manage and inform those end-party teams or any third-party companies if their app is vulnerable at this point and make it fix.
The second part of services is around the web, cloud and other areas. A lot of enterprises or smaller companies want a single vendor offering everything. So we have partnered with other companies that offer web, cloud and all. And we position it as front-ending all of it along with our partners across and we do work with these MSSPs and channels. They sell our mobile app security and we sell their web, cloud and everything. And that enables overall bigger ticket size business for us as well and also exposure to their clientele by giving our mobile app security suit to them.
Q7. Can you name some of these enterprise customers in India and the region? And how has been the growth and demand for Appknox in the last year or so?
Harshit Agarwal: So in India, we work with Yes Bank, Axis Bank, ICICI Bank and Kotak Securities. Apart from these banks, we do work with Zensar and a few other enterprises. We do work with four banks in the Middle East through our channel partners in that region and other banks globally. Besides, we work with airlines and companies in FMCG, energy and IT space as well as some government agencies in UK and Europe through third-party channel partners.
So if I talk specifically about the last one and a half years, the growth has been exponential. Overall we were growing at a decent 1.5 to 2X year-on-year. But last year specifically, it’s been upwards of 2.5 X. Not only that, a lot of enterprises that we are interacting with these days, have realized that mobile app security is important, specifically in government agencies. So the government segment had opened up for us a year ago only. We closed our first government ministry in the Middle East almost a year ago.
Post that deal, we almost closed 7 or 8 ministries last year, including one in India and a few in the Middle East and Europe. So ministries have realized that those end customers or people will use many mobile apps. We help them manage the number of apps and that’s our expertise.
Q8. Is mobile app security testing yet to mature? Where do you see it is moving currently?
Harshit Agarwal: Mobile app testing is mature but when it comes to overall enterprises, I think they’re still in the transition to make it part of DevOps as a whole. DevSecOps has picked up in the last 2 to 3 years. And as per Gartner, by 2023-24, DevSecOps would become part of that hype in HypeCycle and it will be the normal thing every enterprise will be or is already doing. But, at the moment, the transition is going on.
Enterprises have started looking at security as part of DevOps. So it’s not mobile security but the entire security thing, which is now getting portion to DevOps as much as it can be, and that transition is going on in mobile as well. But when it comes to the whole application security suit and mobile app security as an offering, the majority of enterprises are realizing it or have started taking it a little more seriously.
Q9. How is the competition playing in this space?
Harshit Agarwal: We face competition from product-based and services-based companies, but the majority comes from product-based competitors. There are two players in the US, very focused on mobile security. The differentiator against them is that we have set up a device farm in Singapore and India, where we have these real devices that customers interact with versus they use simulators.
A simulator is not a real device but an image of the device, so it has limitations. For example, a banking app is SIM-card dependent as it has to send SMS to verify two-factor authentication (2FA). But in the simulator, there won’t be a SIM card and so it cant send SMS.
For a bank in the Middle East, we have deployed real devices on the location to perform 2FA during testing. Similarly, for a ministry in the Gulf region, we have deployed a device with a SIM card for on-premise app testing with 2FA. We have a real device farm for testing, that’s the key differentiator. While our competitors use the simulator, which is an image form of the device and not a real device to run on the apps; so there are challenges like they cannot do 100% testing, which makes us a little different.
And that took us maximum time in building (platform) what we have today. It took us almost two and a half years from our inception to come up with our platform’s first look and feel, which was heavy on engineering. We had to invent and reinvent many things about how to do mobile app security testing. So it’s an engineering-heavy product we have that differentiates us against our competitors.
Services-based companies are the second set of competitors, where we have automated services, and they have manual ones. And that gives us the speed against them as we have automated 80% of processes. Also, we have managed to balance that with our partner companies. We offer a white-label automated platform to partners to cater to their end cust our objective is that within five years, every mobile app that goes through security testing should have used Appknox for testing. That’s the vision we are driving and opening it up for channel partners and MSSPs to start using our platform and deliver their end customer-secured app at a faster pace.
Q10. Lastly, how does Appknox drive its business?
Harshit Agarwal: We are very heavily channel-driven. I think roughly 50 to 60% of our revenue comes from the channel and the rest 40% of revenue is direct. We have channel partners in Indonesia. Cybersecurity service provider RML (Raditya Mulia Lestari) is one of them, with whom we have worked with three top banks in Indonesia — BCA (Bank Central Asia), Bank of Mandiri and others.
Similarly, in the Middle East, we work with 5 to 6 channel partners, including Paramount Computer Systems and a few more, which has helped us close these government agencies and banks in that region. Also, we work with three-channel partners in Africa and one channel partner each in Latin and Europe. Likewise, we have one channel partner in Sri Lanka and Bangladesh. So these are some geographies where we are working with them to cater to local clients.
(Watch this entire conversation with Appknox’s Harshit Agarwal on TechHerald YouTube channel)